 Mindset docs
Security
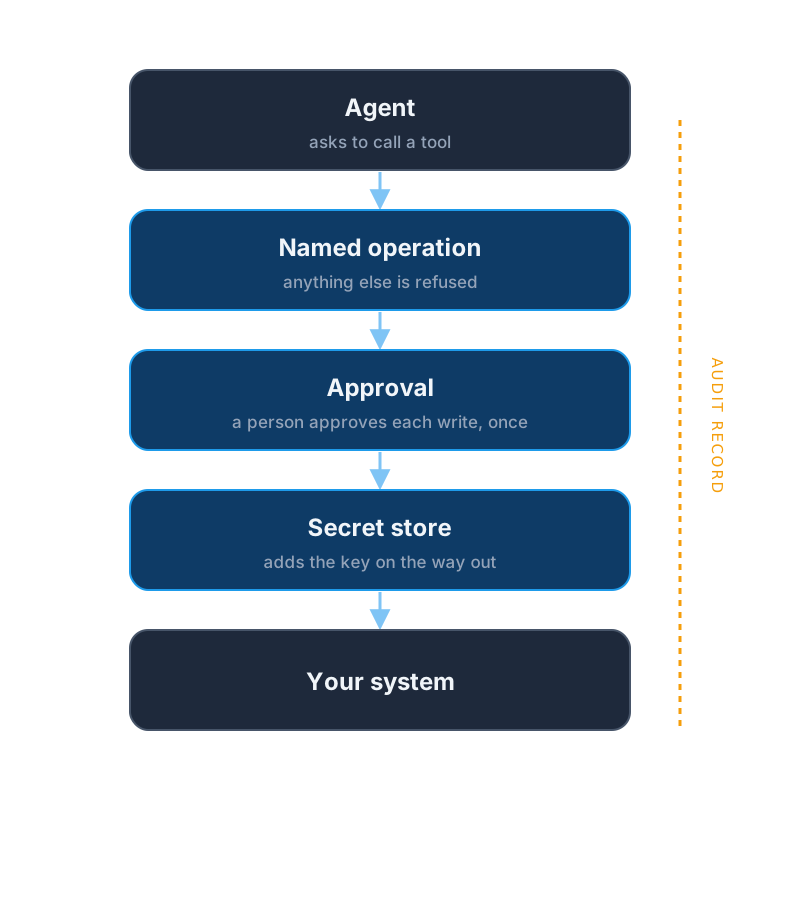
The platform enforces the rules, whatever the prompt says.
- Agents reach your systems only through named operations
- No agent can approve a write
- Keys never reach the agent or the model
- Every action goes into a hash-chained record
Speaker notes
There is no general web access, so even a misled agent can only do what its operations allow. Writes need a person’s approval once per operation, unless the org leaves automatic approval on, which is the default. Credentials live in a secret store and are added on the way out. The audit record is append only and hash-chained, and maps to SOC 2, GDPR, ISO 42001, HIPAA and the EU AI Act. Personal data protection swaps personal details for placeholders before the provider sees them; it is off until an admin turns it on, and it never blocks.